web analytics

Learn AI With Kesse | Best Place For AI News

We make artificial intelligence easy and fun to read. Get Updated AI News.

Satya Nadella Warns Many Critical Infrastructures Are ‘Unpatchable’ Amid AI Cyberattack Concerns
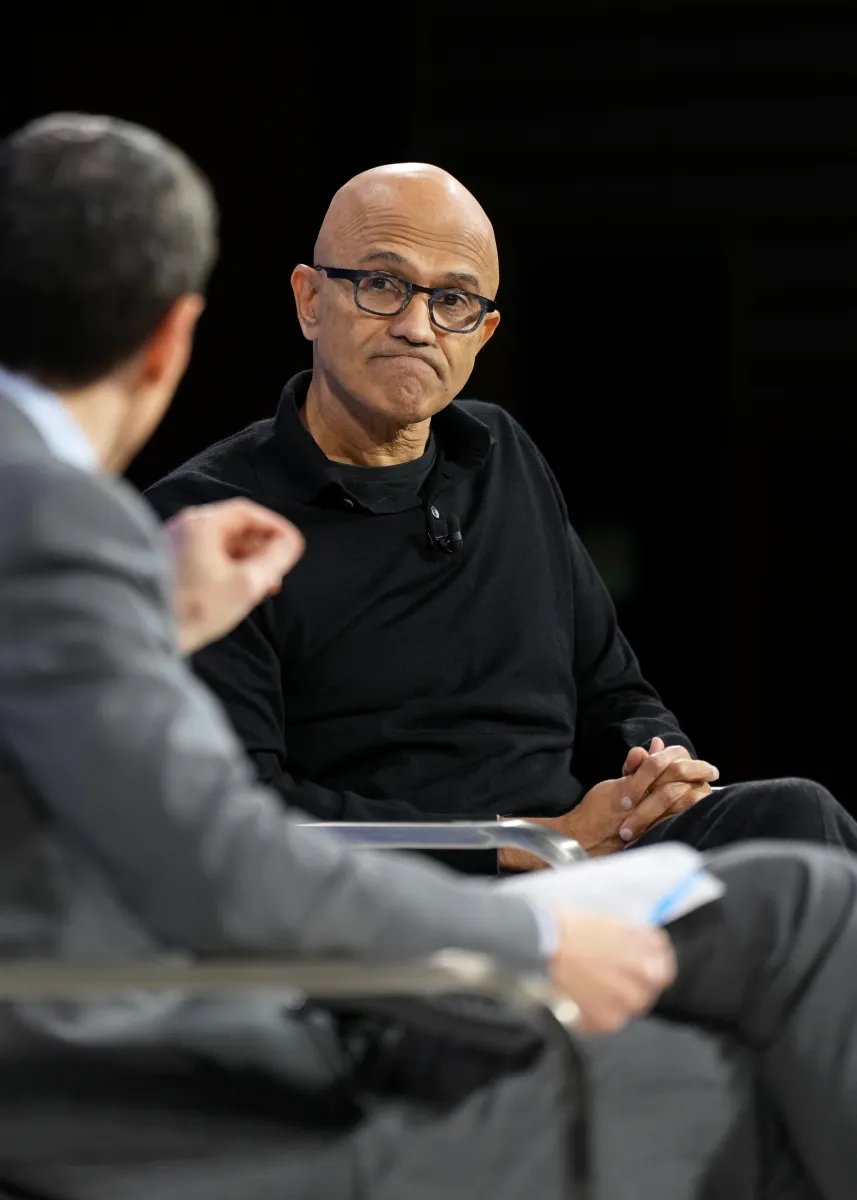
Amidst fears of AI cyberattacks, Satya Nadella says lots of critical infrastructure is 'unpatchable'

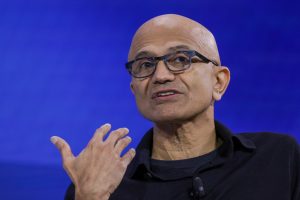
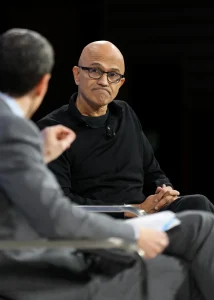
Image Credits:Adam Gray/Getty Images for The New York Times

The State of America’s Software Vulnerabilities: Insights from Microsoft CEO Satya Nadella

During a recent appearance at The New York Times’ DealBook Summit, Microsoft CEO Satya Nadella expressed deep concern over the numerous unfixable software vulnerabilities that afflict America’s critical infrastructure. This includes not just the software that underpins everyday hardware but also vital transportation systems. In an era increasingly marked by AI-aided cyberattacks, these vulnerabilities pose a growing threat.

Unpatchable Vulnerabilities in Critical Infrastructure

Nadella pointed out that many components of America’s critical infrastructure are essentially “unpatchable.” He highlighted various systems, such as firmware, chillers, and HVAC (Heating, Ventilation, and Air Conditioning) systems, emphasizing that these devices are connected to the internet. As a result, they are at risk of being exploited.

“The smartification of the economy,” as Nadella described it, refers to the integration of “dumb” devices with the internet, a shift that, while beneficial in many ways, has introduced significant security challenges.

Recent Outages and Their Implications

Nadella’s remarks came in light of a series of widespread outages affecting Microsoft Outlook, the NSA, the FAA, and Apple. While speculation about cyberattacks being responsible for these outages circulated, officials have refuted these claims. Nonetheless, the rise of AI-enabled cyberattacks is compelling companies to rethink their strategies for identifying and fixing vulnerabilities.

In discussing the recent Outlook outage, Nadella noted that it stemmed from a “latent bug” leading to a “perfect storm” of issues. He assured the audience that Microsoft was taking this incident seriously and would incorporate lessons learned into future preventive measures.

The Challenge of Vulnerability Management

Nadella also commented on the vulnerabilities present in transportation systems, highlighting the abundance of discoverable yet unpatchable firmware. The need for significant modernization in these systems has never been more urgent. He stressed the importance of assessing threat vectors and enhancing capabilities for real-time defense and detection.

One critical point Nadella made was that while the tools available to identify vulnerabilities have become increasingly powerful, the pace at which patches must be deployed has also accelerated dramatically. “We now have a very powerful tool that finds vulnerabilities,” he stated. However, the speed of patching has outstripped the time companies previously enjoyed to test and understand these patches.

The Instability of Rapid Patch Deployment

Nadella described a scenario where instances like “patch 1795093770” must be immediately deployed into production environments as they are actively being exploited. This urgent need for swift action can lead to instability across systems as organizations scramble to address vulnerabilities.

The Future of Cybersecurity and Infrastructure Modernization

As Nadella pointed out, organizations must modernize their critical infrastructure to handle the vulnerabilities inherent in their systems. This modernization involves not just adopting new technologies but also reevaluating how they approach the detection and remediation of vulnerabilities.

The rapid evolution of AI technologies, which simplifies the execution of sophisticated cyberattacks, adds a layer of complexity to this challenge. Cybersecurity needs to adapt just as quickly to ensure that systems are not only patched but also resilient against potential threats.

Concluding Thoughts

The discussions led by Satya Nadella at the DealBook Summit underscore a crucial point: the landscape of cybersecurity is evolving rapidly, and organizations must rise to the occasion. Awareness of unpatchable vulnerabilities is only the first step; the next is implementing robust, forward-thinking strategies to mitigate risks.

The intersection of AI and cybersecurity is a double-edged sword, offering tools for both attackers and defenders. As companies work to modernize their infrastructure and refine their vulnerability management processes, a proactive rather than reactive approach may prove essential for safeguarding America’s critical systems.

The Road Ahead

Going forward, organizations will need to reassess not only their infrastructure but also their overall cyber-risk management strategies. Collaboration across sectors and industries may also become increasingly necessary as the stakes continue to rise. Cybersecurity is no longer simply a technical issue; it is a critical business concern that demands attention from the highest levels of management.

In summary, the remarks from Microsoft CEO Satya Nadella reflect a broader recognition of the challenges posed by unpatchable systems and AI-driven threats. As the digital landscape continues to evolve, so must our approach to cybersecurity, ensuring that we can effectively navigate the complexities of today’s interconnected world.

Thanks for reading. Please let us know your thoughts and ideas in the comment section down below.

Source link
#fears #cyberattacks #Satya #Nadella #lots #critical #infrastructure #unpatchable

About The Author

Leave a Reply

Your email address will not be published. Required fields are marked *

We use cookies to personalize content and ads and to primarily analyze our geo traffic sources. We also may share information about your use of our site with our social media, advertising, and analytics partners to improve your user experience. We respect your privacy and will never abuse your information. [ Privacy Policy ] View more
Cookies settings
Accept
Decline
Privacy & Cookie Policy
Privacy & Cookies policy
Cookie name Active

The content on this page governs our Privacy Policy. It describes how your personal information is collected, used, and shared when you visit or make a purchase from learnaiwithkesse.com (the "Site").

Kesseswebsites and Advertising owns Learn AI With Kesse and the website learnaiwithkesse.wiki. For the purpose of this Terms and Agreements [ we, us, I, our ] represents the owner of Learning AI With Kesse which is Kesseswebsites and Advertising. [ You, your, student and buyer ] represents you as the user and visitor of this site. Terms of Conditions, Terms of Service, Terms and Agreement and Terms of use shall be considered the same here. This website or site refers to https://learnaiwithkesse.com. You agree that the content of this Terms and Agreement may include Privacy Policy and Refund Policy. Products refer to physical or digital products. This includes eBooks, PDFs, and text or video courses. If there is anything on this page you do not understand you agree to reach out to us via email [ emmanuel@learnaiwithkesse.com ] for explanation before using any part of this site.

1. Personal Information We Collect

When you visit this Site, we automatically collect certain information about your device, including information about your web browser, IP address, time zone, and some of the cookies that are installed on your device. The primary purpose of this activity is to provide you a better user experience the next time you visit our again and also the data collection is for analytics study. Additionally, as you browse the Site, we collect information about the individual web pages or products that you view, what websites or search terms referred you to the Site, and information about how you interact with the Site. We refer to this automatically-collected information as "Device Information."

We collect Device Information using the following technologies:

"Cookies" are data files that are placed on your device or computer and often include an anonymous unique identifier. For more information about cookies, and how to disable cookies, visit http://www.allaboutcookies.org. To comply with European Union's GDPR (General Data Protection Regulation), we do display a disclaimer a consent text at the bottom of this website. This disclaimer alerts you the visitor or user of this website about why we use cookies, and we also give you the option to accept or decline. If you accept for us to use cookies on your site, the agreement between you and us will expire after 180 has passed.

"Log files" track actions occurring on the Site, and collect data including your IP address, browser type, Internet service provider, referring/exit pages, and date/time stamps.

"Web beacons," "tags," and "pixels" are electronic files used to record information about how you browse the Site.

Additionally, when you make a purchase or attempt to make a purchase through the Site, we collect certain information from you, including your name, billing address, shipping address, payment information (including credit card numbers), email address, and phone number. We refer to this information as "Order Information."

When we talk about "Personal Information" in this Privacy Policy, we are talking both about Device Information and Order Information.

Payment Information

Please note that we use 3rd party payment processing companies like https://stripe.com and https://paypal.com to process your payment information. PayPal and Stripe protects your data according to their terms and agreement and may store your data to help make your subsequent transactions on this website easier. We never and [ DO NOT ] store your card information or payment login information on our website or server. By making payment on our site, you agree to abide by the Terms and Agreement of the 3rd Party payment processing companies we use. You can visit their websites to read their Terms of Use and learn more about them.

2. How Do We Use Your Personal Information?

We use the Order Information that we collect generally to fulfill any orders placed through the Site (including processing your payment information, arranging for shipping, and providing you with invoices and/or order confirmations). Additionally, we use this [a] Order Information to:

[b] Communicate with you;

[c] Screen our orders for potential risk or fraud; and

When in line with the preferences you have shared with us, provide you with information or advertising relating to our products or services. We use the Device Information that we collect to help us screen for potential risk and fraud (in particular, your IP address), and more generally to improve and optimize our Site (for example, by generating analytics about how our customers browse and interact with the Site, and to assess the success of our marketing and advertising campaigns).

3. Sharing Your Personal Information

We share your Personal Information with third parties to help us use your Personal Information, as described above. For example, we use System.io to power our online store--you can read more about how Systeme.io uses your Personal Information here: https://systeme.io/privacy-policy/ . We may also use Google Analytics to help us understand how our customers use the Site--you can read more about how Google uses your Personal Information here: https://www.google.com/intl/en/policies/privacy/. You can also opt-out of Google Analytics here: https://tools.google.com/dlpage/gaoptout.

Finally, we may also share your Personal Information to comply with applicable laws and regulations, to respond to a subpoena, search warrant or other lawful request for information we receive, or to otherwise protect our rights.

4. Behavioral Advertising

As described above, we use your Personal Information to provide you with targeted advertisements or marketing communications we believe may be of interest to you. For more information about how targeted advertising works, you can visit the Network Advertising Initiative’s (“NAI”) educational page at http://www.networkadvertising.org/understanding-online-advertising/how-does-it-work.

You can opt-out of targeted advertising by:

COMMON LINKS INCLUDE:

FACEBOOK - https://www.facebook.com/settings/?tab=ads

GOOGLE - https://www.google.com/settings/ads/anonymous

BING - https://advertise.bingads.microsoft.com/en-us/resources/policies/personalized-ads]

Additionally, you can opt-out of some of these services by visiting the Digital Advertising Alliance’s opt-out portal at: http://optout.aboutads.info/.

5. Data Retention

Besides your card payment and payment login information, when you place an order through the Site, we will maintain your Order Information for our records unless and until you ask us to delete this information. Example of such information include your first name, last name, email and phone number.

6. Changes

We may update this privacy policy from time to time in order to reflect, for example, changes to our practices or for other operational, legal or regulatory reasons.

7. Contact Us

For more information about our privacy practices, if you have questions, or if you would like to make a complaint, please contact us by e-mail at emmanuel@learnaiwithkesse.com or by mail using the details provided below:

8. Your acceptance of these terms

By using this Site, you signify your acceptance of this policy. If you do not agree to this policy, please do not use our Site. Your continued use of the Site following the posting of changes to this policy will be deemed your acceptance of those changes.

Last Update | 18th August 2024

Save settings
Cookies settings